---
title: Cycle Steps Identified as SQL Injection
description: A recently identified vulnerability is incorrectly identifying certain Cycle test steps as a high severity SQL injection threat.
---
[Skip to content](https://kb.cyclelabs.io/cycle-steps-identified-as-sql-injection#main-content)
English - United States
Show submenu for translations
Open main navigation
Close main navigation
- English - United States
Show submenu for translations
- [Get Support & Track Tickets](https://help.cyclelabs.io/)
[Get Support & Track Tickets](https://help.cyclelabs.io/?hsLang=en-us)
How can we help you?
- There are no suggestions because the search field is empty.
1. [Cycle Knowledge Base](https://kb.cyclelabs.io/?hsLang=en-us)
2. [Common Issues](https://kb.cyclelabs.io/common-issues?hsLang=en-us)
# Cycle Steps Identified as SQL Injection
## A recently identified vulnerability is incorrectly identifying certain Cycle test steps as a high severity SQL injection threat.
We have seen several instances of Cycle test steps such as the MOCA connection step being flagged as SQL Injection by some firewalls.
### Example
Execution of the step :
```
Given I connect to MOCA at " " logged in as " " with password " "
```
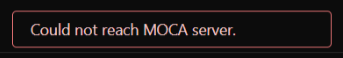
May display this error below in Cycle even though you are able to confirm MOCA connectivity outside of Cycle:
> 
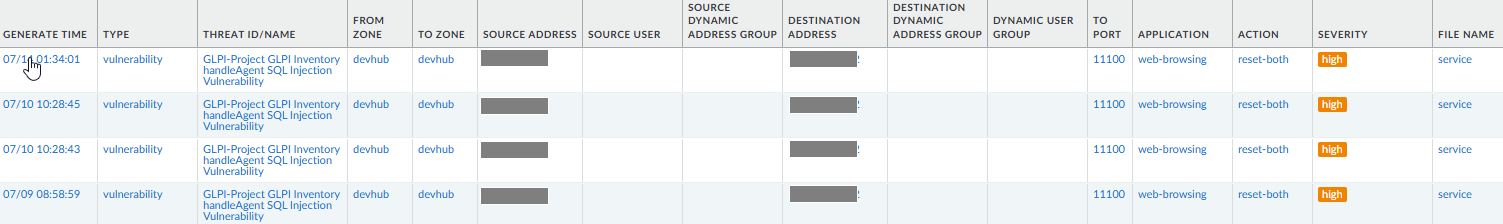
Your organization's firewall may be reporting a threat detection similar to the one below:
> 
### Vulnerability Details
The specific vulnerability that is flagging Cycle as SQL injection is **CVE-2025-24799**
Additional information about this specific CVE can be found at this [link](https://www.cve.news/cve-2025-24799/).
### Resolution
The Cycle labs Product Development team is working to identify the root cause of this issue.
Our goal is to incorporate a long term fix to Cycle that will prevent this CVE from identifying Cycle steps as attempts at SQL injection.
We will update this article with a Cycle version number and projected release date once we have identified a fix and scheduled the Cycle version release.
In the meantime, your organization's network security team will need to put an override of **CVE-2025-24799** in place in order to use the Cycle steps that are flagged as SQL injection.
Depending on the firewall used by you organization, options for overriding the CVE may allow scoping the override to a specific set of IP addresses to only allow devices running Cycle tests to override the CVE threat detection.
We understand that overriding a CVE is not the optimal solution, and we are working diligently to provide the long term solution.
If you have any questions or concerns about this issue or placing an override on the CVE, please reach out to [help@cyclelabs.io](mailto:help@cyclelabs.io), and we will assist you as you engage your network security team for resolution.
- [Getting started](https://kb.cyclelabs.io/getting-started?hsLang=en-us)
- [Using Cycle with BYWMS](https://kb.cyclelabs.io/using-cycle-with-bywms?hsLang=en-us)
- [Cycle Appliance and CI/CD](https://kb.cyclelabs.io/cycle-appliance-and-ci-cd?hsLang=en-us)
- [Tips and Tricks](https://kb.cyclelabs.io/tips-and-tricks?hsLang=en-us)
- [Native App](https://kb.cyclelabs.io/native-app?hsLang=en-us)
- [Deprecated Steps](https://kb.cyclelabs.io/deprecated-steps?hsLang=en-us)
- [Common Issues](https://kb.cyclelabs.io/common-issues?hsLang=en-us)
[](http://cyclelabs.io)
[mailto:email@email.com](mailto:email@email.com)
Copyright © 2026, Cycle Labs